
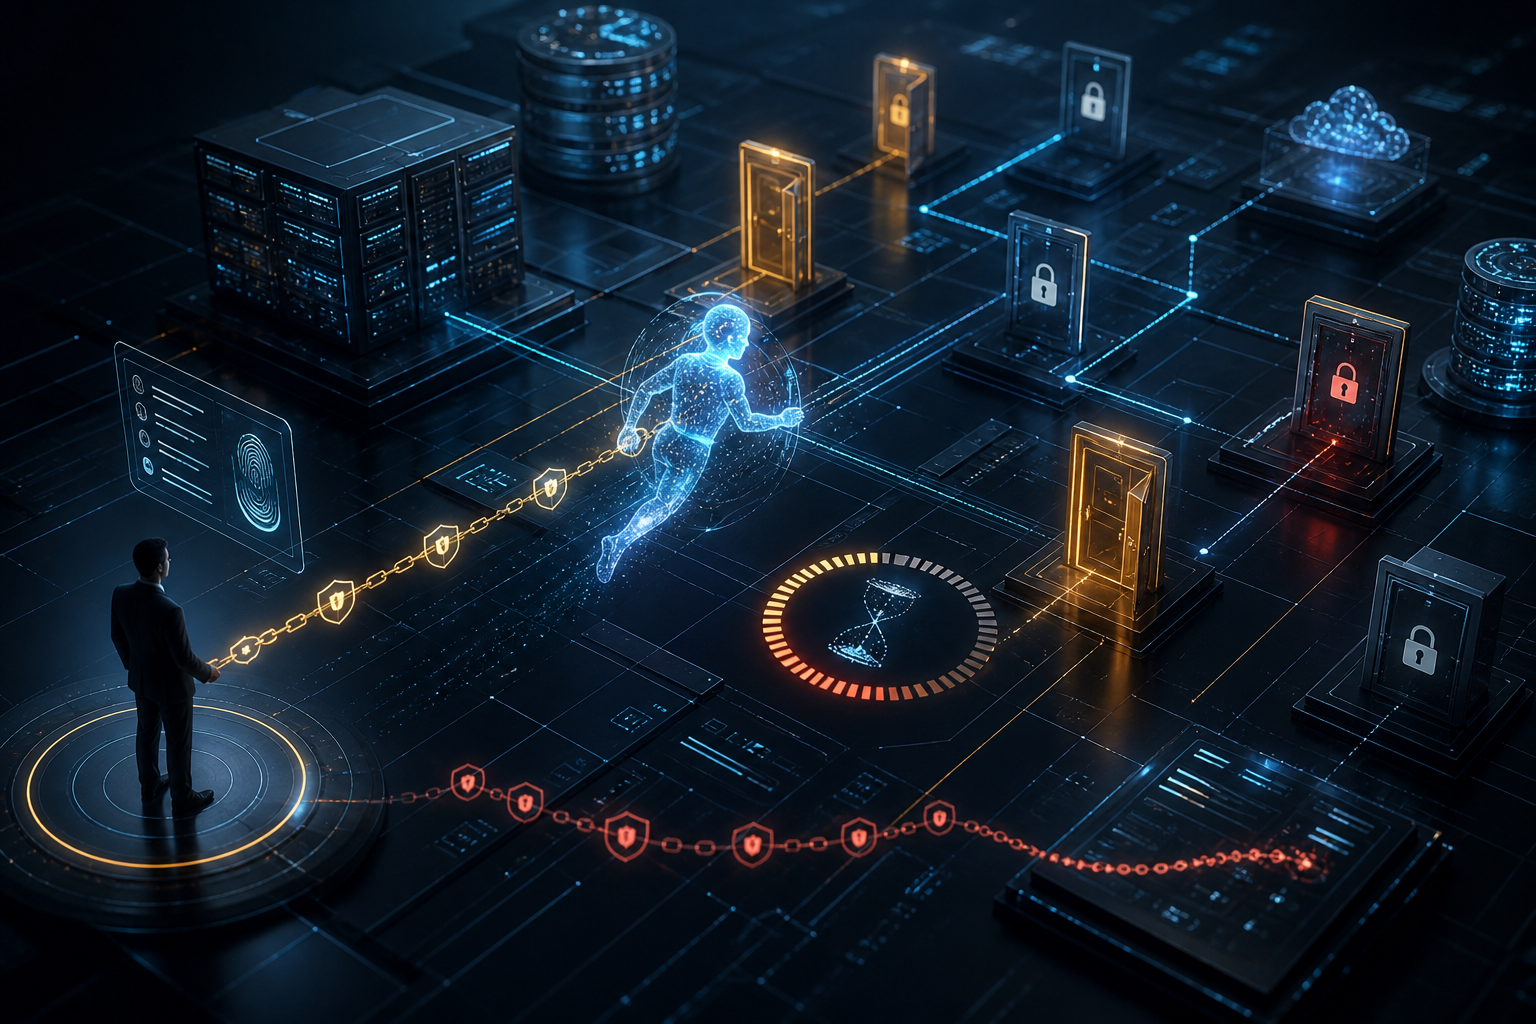
Identity alone cannot tell us what an autonomous system should be allowed to do.
As AI agents begin acting across enterprise systems, cybersecurity faces a new trust problem. Identifying the agent is only the beginning; organisations also need to establish whose authority it carries, what that authority permits and when it should end.
Cybersecurity has spent decades improving the controls around access. Users authenticate themselves, permissions determine which systems they can reach, privileged accounts receive additional protection and activity is recorded so organisations can establish what happened when something goes wrong.
AI agents complicate that model because the entity accessing a system may no longer be the person who has the authority to use it. An employee might ask an agent to analyse customer information, retrieve documents, update a record or complete a business process. The agent may then interact with several applications, call APIs and make decisions about which steps are necessary. The employee remains behind the original request, but software is now exercising some degree of authority on their behalf.
That changes the security question. Establishing the identity of the agent still matters, but organisations also need to know where its authority came from, what that authority permits and whether it should continue as the agent moves between systems and performs different actions.
Identity is only the starting point
Cybersecurity already manages enormous numbers of non-human identities. Applications use service accounts, machines use certificates, APIs use tokens and automated processes rely on credentials to communicate with other systems. AI agents will use many of the same mechanisms, but autonomous behaviour introduces another dimension.
A conventional service account generally performs a predictable function, allowing its permissions to be designed around a relatively stable set of actions. An AI agent may instead determine how to achieve an objective, choose between tools and alter its sequence of operations according to context. The credentials may look familiar to security teams, but the behaviour behind them is potentially much more dynamic.
The distinction has attracted the attention of the US National Institute of Standards and Technology, which is examining how existing identity standards and practices can be applied to software and AI agents. Its work identifies identification, authorisation, auditing and non-repudiation among the areas that need to be considered as agents gain access to enterprise data, applications and tools.
This pushes the problem beyond proving that an agent is what it claims to be. Identity establishes the actor, but it does not by itself establish what that actor should be entitled to do, particularly when the authority originated with someone else.
Authority cannot simply be inherited
Consider an employee who has permission to view financial information and asks an AI agent to analyse a particular account. Giving the agent access to the information may be necessary to complete the task, but it does not follow that the agent should inherit every permission belonging to that employee. Nor should permission necessarily persist once the task is complete.
An agent might be allowed to retrieve a customer record but not alter it, prepare a payment but not release it, or analyse information from one system without transferring it into another. If another agent or service becomes involved, the organisation also needs to preserve the chain connecting those actions to the authority behind the original request.
This makes least privilege considerably more dynamic. Instead of determining only which resources an identity can access, organisations increasingly need to determine what authority an agent requires for a particular task, in a particular context and for a particular period.
Current enterprise controls are not necessarily ready for that distinction. Okta’s 2026 research among CISOs and security executives found that fewer than half were confident they could identify all AI agents operating in their environments, centrally control what those agents could access or authorise what individual agents were allowed to do. Some organisations were still relying on shared credentials or broadly permissioned service accounts to govern agent access.
These are familiar cybersecurity weaknesses, but autonomy changes their potential consequences. Excessive permissions attached to a human account are dangerous; excessive permissions available to software capable of operating continuously, moving between systems and taking actions at machine speed create a different scale of exposure.
Trust needs an expiry date
Human access management has traditionally worked around relatively persistent relationships. Someone joins an organisation, receives permissions according to their role and retains them until their responsibilities change or they leave. An AI agent, by contrast, might legitimately require access for a single task lasting only a few minutes.
That makes the duration of authority part of the security decision. Access granted to analyse a customer account should not automatically remain available after the analysis is complete, just as permission to perform one workflow should not silently become permission to perform another.
Revocation consequently becomes more important. If an agent begins behaving unexpectedly, an organisation needs to be able to remove its authority before it can continue acting across connected systems. Okta’s research found that 55% of organisations could revoke agent access within hours following a breach, while organisations with more advanced agentic identity governance were considerably more likely to do so within minutes. For autonomous systems operating at machine speed, even minutes can represent a significant window.
The implication is that access control itself may need to become more dynamic. Identity, context, behaviour and policy could increasingly determine authority continuously rather than permissions being granted once and assumed to remain valid. Trust in an autonomous system would therefore become conditional not only on what it is, but on what it is doing and whether the authority required for that action still exists.
Accountability has to survive autonomy
The chain of authority matters for another reason: organisations ultimately need to know who is responsible for an action. When an employee performs an unauthorised transaction, investigators can examine who authenticated, what permissions they possessed and what they did. If an AI agent performs the transaction, that chain should not disappear simply because software sits between the person and the action.
The audit trail may therefore need to show which agent acted, who or what initiated the task, which authority was delegated, which systems and tools were used and whether another agent participated along the way. This is not about making software accountable in the same sense as a person; it is about preventing autonomy from obscuring human and organisational responsibility.
As agents become embedded in enterprise processes, that traceability becomes part of digital trust. Organisations need to be able to reconstruct not only what happened but why a system had the authority to make it happen.
The principles developed through decades of identity and access management remain essential. Authentication, least privilege, credential protection, logging and revocation all become more important as autonomous systems proliferate, but the relationship between those controls is changing. An authenticated identity does not automatically establish appropriate authority, authority granted for one task should not necessarily apply to another, and permission inherited from a human should not automatically become permanent permission for an agent.
AI agents therefore create a security problem that sits between identity, access and control. Cybersecurity still needs to establish who or what is entering a system, but it increasingly needs to preserve the chain of authority as autonomous software moves through it. Identity tells us what is acting. Trust depends on knowing why it was allowed to act.
Leave a Reply