
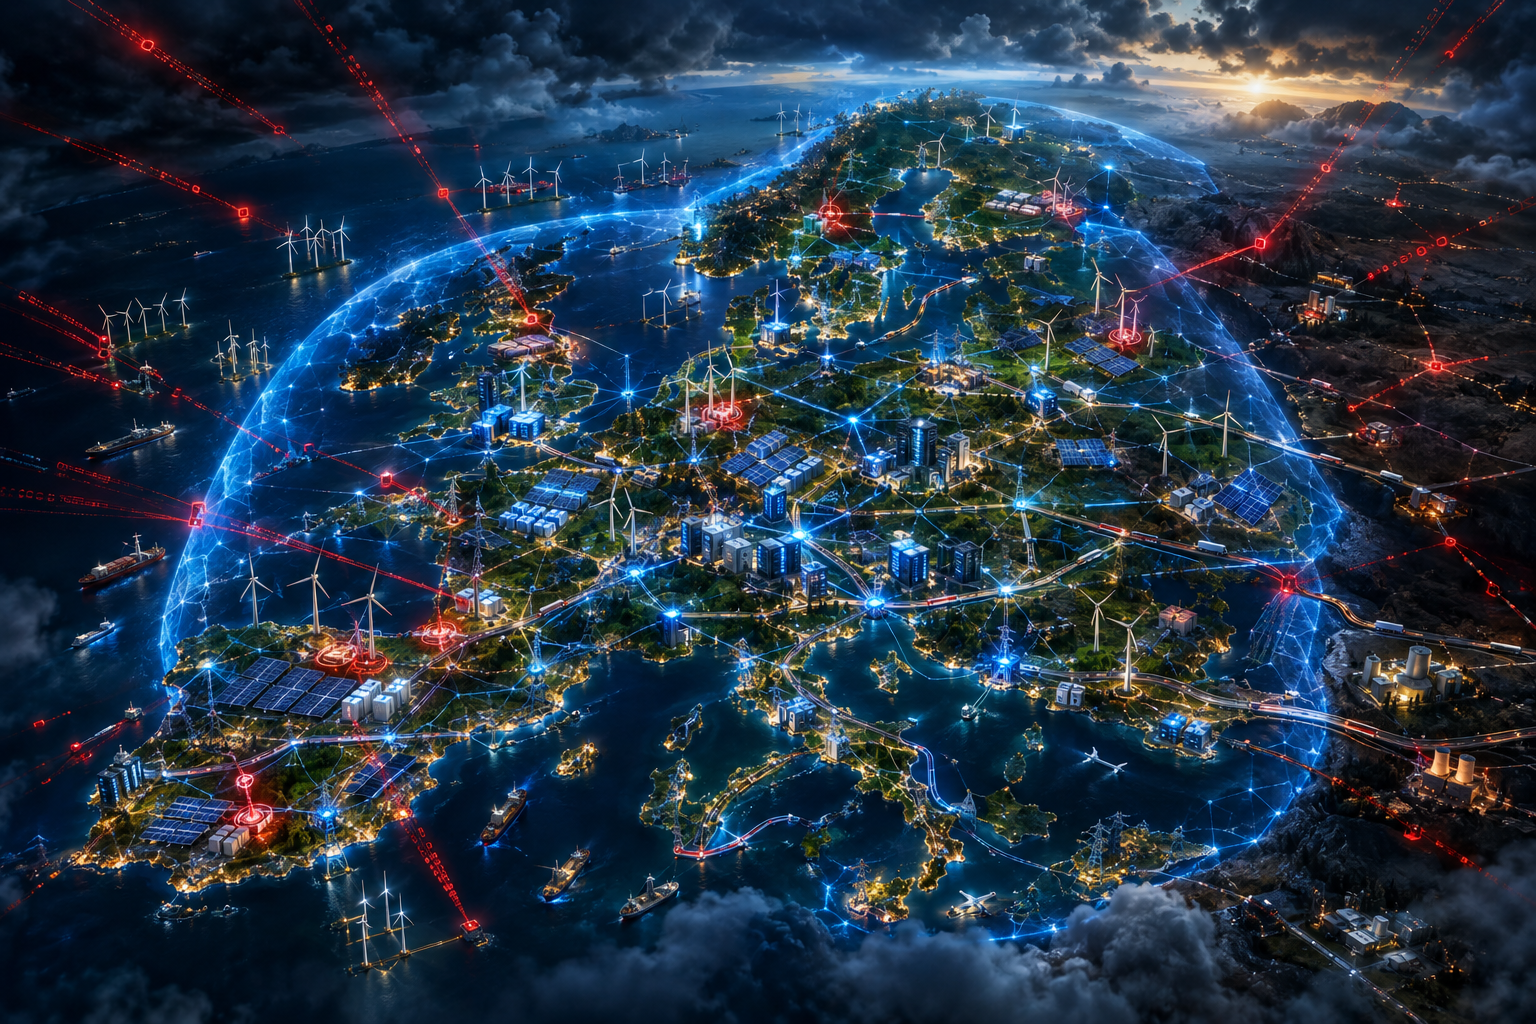
Europe is investing heavily in technological sovereignty, from artificial intelligence and digital identity to cloud infrastructure and industrial innovation. Yet its ability to control its digital future also depends on protecting the energy, transport and communications systems that keep its economy functioning. New evidence of exposed European renewable-energy infrastructure, combined with growing geopolitical tensions and an increasingly complex cyber threat landscape, raises an uncomfortable question: can Europe claim technological sovereignty if it cannot guarantee the resilience of the systems on which that sovereignty depends?
Europe’s infrastructure is becoming an increasingly attractive target
Thousands of wind and solar power systems across Europe have been found exposed to the internet, potentially allowing attackers to access operational interfaces and, in some cases, interfere with electricity generation. The findings, reported on 6 October by Reuters following research involving Dutch cybersecurity specialists Modat and the Netherlands’ National Cyber Security Centre, identified 8,547 exposed systems across 35 European countries.
The researchers identified approximately 181 sites where exposed interfaces could potentially allow more extensive operational control, including switching equipment on or off. Spain, Greece and Germany were among the countries with the largest numbers of affected installations. Although exposure does not necessarily mean that a system has been compromised, the findings demonstrate how the increasing connectivity of Europe’s energy infrastructure can introduce vulnerabilities extending beyond conventional information technology.
The discovery comes at a particularly sensitive moment. Europe’s energy systems are becoming more distributed, with renewable generation, smart grids, storage systems and digitally connected equipment creating new opportunities for efficiency and flexibility. These developments are essential to the continent’s energy transition, but they also increase the number of connected components that must be secured and monitored.
The implications extend well beyond the energy industry. Electricity underpins telecommunications, transport, manufacturing, healthcare and the digital services on which modern economies depend. A successful attack on operational infrastructure can therefore produce consequences that are considerably more disruptive than the theft of information or the temporary unavailability of a business application.
For Europe, the issue is becoming increasingly connected to technological sovereignty. Developing and operating digital infrastructure is important, but maintaining control over that infrastructure when it comes under attack may prove an equally significant test.
When disruption becomes the objective
Cybersecurity has traditionally been associated with protecting information, preventing unauthorised access and maintaining the confidentiality, integrity and availability of digital systems. These objectives remain fundamental, but the threat landscape facing critical infrastructure introduces additional considerations.
Financially motivated cybercrime continues to account for a substantial proportion of malicious activity. Ransomware, data theft and extortion remain serious threats, frequently causing significant operational disruption even when disruption is not the attacker’s primary objective.
However, geopolitical conflict, sabotage and politically motivated attacks introduce a different dimension. In these circumstances, interruption of essential services may be the intended outcome rather than a consequence of another criminal activity. The objective may be to undermine public confidence, damage economic activity, interfere with industrial operations or place pressure on governments and institutions.
The distinction matters because the defensive priorities are not necessarily identical. Protecting sensitive information and restoring compromised computer systems may be sufficient for some conventional cyber incidents. Industrial environments can require a different response, particularly when digital systems control physical equipment or processes that cannot simply be restarted without consequences.
A manufacturing facility may depend on carefully coordinated production systems, while an electricity distribution network must maintain stability across interconnected infrastructure. Interruptions can affect equipment, safety, supply chains and essential services long after the original intrusion has been contained.
This makes operational continuity a central consideration. The question is not only whether an attacker can be prevented from entering a system, but whether the organisation can maintain essential functions and recover safely if its defences are breached.
ENISA’s warning about Europe’s dependencies
The European Union Agency for Cybersecurity’s 2026 Threat Landscape provides important context for these concerns. Published in September, the report examines cyber incidents and events observed during 2025 and highlights the increasing significance of technological dependencies, geopolitical developments and attacks against essential services.
ENISA found that 73% of the organisations targeted in the events analysed were classified as essential or important entities under the NIS2 framework. Public administration accounted for the largest share of recorded targeting, followed by sectors including business services, transport, manufacturing and financial services.
The findings should not be interpreted as evidence that every incident involved sophisticated sabotage or an attempt to disrupt physical infrastructure. Much of the activity reflected familiar cybercrime, distributed denial-of-service attacks and politically motivated campaigns. Nevertheless, the concentration of targeting among organisations responsible for important services demonstrates why operational resilience has become a central European security concern.
ENISA also identifies the expanding attack surface created by digital dependencies. Organisations increasingly rely on interconnected technology providers, cloud services, software platforms and industrial systems, creating relationships in which vulnerabilities can extend beyond the boundaries of an individual organisation.
For critical infrastructure operators, these dependencies introduce an additional challenge. Security cannot be considered exclusively at the level of a single facility or technology platform when essential operations depend on external communications networks, software suppliers, equipment manufacturers and service providers. The resilience of the wider ecosystem becomes part of the organisation’s own security posture.
From centralised grids to distributed risk
The changing architecture of Europe’s energy infrastructure illustrates the challenge particularly clearly. Traditional electricity systems were built around relatively centralised generation and distribution models, with large power stations supplying energy through established transmission and distribution networks.
The transition towards renewable energy is changing that structure. Solar installations, wind farms, battery storage, distributed generation and demand-response systems introduce new participants and increasingly complex interactions between electricity producers, network operators and consumers.
Digital connectivity is fundamental to managing this environment. Monitoring systems, remote controls, forecasting applications and automated grid-management technologies allow operators to coordinate distributed resources and respond to changing conditions. However, these capabilities also create additional pathways through which an attacker might attempt to influence operational systems.
The issue was central to the ninth European Cybersecurity Energy Forum, held in Brussels on 8 October and jointly organised by ENISA, the Association of European Distribution System Operators, the European Energy Information Sharing and Analysis Centre and the European Network for Cyber Security.
The forum focused on grid resilience and preparedness in a changing geopolitical and technological environment. Its organisers highlighted the increasing complexity of distributed energy systems, the expansion of cyber threats and the growing dependencies on global supply chains.
Their emphasis reflects a broader shift in industrial cybersecurity. Preparing to prevent attacks remains essential, but infrastructure operators must also develop the capacity to manage incidents while maintaining critical services.
The discovery of exposed renewable-energy systems earlier in the same week illustrates why this distinction matters. A distributed energy network may contain thousands of individually managed components, making consistent security practices, visibility and coordinated incident response more difficult to achieve.
Regulation provides a framework, but not a guarantee
Europe has responded to the changing threat environment through a growing body of cybersecurity and resilience legislation. The NIS2 Directive expands cybersecurity risk-management and incident-reporting requirements across a wider range of essential and important entities, while strengthening expectations concerning management responsibility, supply-chain security and business continuity.
The Critical Entities Resilience Directive complements this approach by addressing the wider resilience of essential services against physical, natural and human-made threats. Together, the frameworks recognise that maintaining critical infrastructure requires more than protecting information systems against unauthorised access.
The European Union has also developed mechanisms intended to improve cooperation during significant cross-border cybersecurity incidents, including the European Cyber Crises Liaison Organisation Network, EU-CyCLONe.
These initiatives establish important responsibilities and coordination mechanisms, but their effectiveness depends on implementation. Regulatory compliance can encourage better risk management and provide a basis for accountability, yet it cannot eliminate vulnerabilities or guarantee that essential services will remain available during a serious incident.
Industrial operators must translate regulatory requirements into practical capabilities, including network segmentation, secure remote access, vulnerability management, incident exercises, supplier assurance and recovery procedures appropriate to operational technology environments.
In many cases, this requires closer cooperation between information technology teams, operational engineers, equipment manufacturers and executive management. Decisions about cybersecurity controls must take account of industrial processes, equipment lifecycles and the consequences of interrupting essential operations.
The challenge is particularly demanding for infrastructure that combines modern connected technology with equipment designed to remain in service for decades.
Technological sovereignty depends on resilience
Europe’s ambitions for technological sovereignty are frequently discussed in terms of reducing dependence on external technology providers, strengthening domestic innovation and developing greater control over digital infrastructure.
These objectives are significant, particularly as artificial intelligence, cloud computing and digital identity become increasingly important to economic competitiveness and public administration. However, sovereignty also has an operational dimension that can receive less attention.
A European organisation may own its infrastructure, operate its own software and comply with European regulations while remaining dependent on external components, communications networks, energy supplies and technology providers.
These dependencies are not inherently undesirable. International supply chains and interconnected systems are fundamental to modern industry. The strategic question is whether critical dependencies are understood, managed and supported by credible alternatives or recovery arrangements.
For Europe’s energy infrastructure, this includes the ability to maintain essential functions when individual systems are compromised or unavailable. For manufacturing, it means understanding how attacks against connected equipment, suppliers or operational networks could affect production. For telecommunications and digital services, it requires resilience across the physical and software infrastructure that supports connectivity.
Sovereignty in this context cannot reasonably mean complete technological self-sufficiency. It is better understood as the capacity to retain meaningful control over essential functions, manage critical dependencies and maintain the ability to act when external conditions become unfavourable. Cybersecurity becomes an essential part of that capacity.
Responsibility moves beyond the security department
The growing importance of infrastructure resilience also changes the question of responsibility. Cybersecurity teams remain central to identifying vulnerabilities, monitoring threats and responding to incidents, but they cannot independently determine how essential industrial services should operate during a serious disruption.
Those decisions involve engineering, operations, business continuity, suppliers, regulators and executive leadership. They require an understanding of which services must remain available, which systems can be isolated safely and how operations can be restored without creating additional risks.
The integration of artificial intelligence and increasingly autonomous industrial systems adds another dimension. Automated monitoring, predictive maintenance and AI-supported operational decisions may improve efficiency and responsiveness, but they also introduce questions about system authority, human oversight and the consequences of incorrect or manipulated decisions.
As digital technologies acquire greater influence over physical operations, organisations must establish clear boundaries between automated capabilities and operational responsibility.
This is particularly relevant to Europe’s technological sovereignty ambitions. Greater control over the development and deployment of technology must be accompanied by the ability to govern its behaviour, maintain oversight and respond when systems fail or are deliberately compromised. Trust in critical infrastructure is ultimately demonstrated through dependable operation, effective recovery and accountable management.
Europe’s next sovereignty challenge
Europe’s pursuit of technological sovereignty is entering a more demanding phase. Developing competitive AI models, establishing common digital identity infrastructure and strengthening European technology capabilities are important steps towards greater strategic autonomy.
Yet these achievements depend on a foundation of essential services that must remain secure and operational in an increasingly complex threat environment.
The exposure of thousands of renewable-energy systems demonstrates how vulnerabilities can emerge as infrastructure becomes more distributed and digitally connected. ENISA’s latest threat assessment reinforces the importance of managing technological dependencies, while Europe’s cybersecurity and resilience frameworks provide a basis for improving preparedness and coordination.
The challenge now is to turn those frameworks into operational capabilities across industries and national boundaries. No cybersecurity strategy can guarantee that every attack will be prevented, particularly when adversaries are prepared to exploit technical weaknesses, supply-chain dependencies and geopolitical tensions. The more meaningful objective is to ensure that critical systems can withstand disruption, maintain essential functions and recover without surrendering control of their operations.
For Europe, that capability is becoming an increasingly important measure of technological sovereignty. The continent’s digital future will depend on the technologies it can develop and deploy, but its ability to protect and sustain the infrastructure supporting those technologies may ultimately determine how much control it truly possesses.


Leave a Reply